Landing Page & Platform
Health and security checks for open-source npm packages
The Cybersecurity Insights Portal tells engineers how risky an open-source npm package is before they add it. The landing page pitches it to development and SOC teams. It's meant to make package reviews faster and dependency choices safer.
- Client
- Undisclosed
- My role
- UX research, MVP design
- Type
- Web platform and landing page
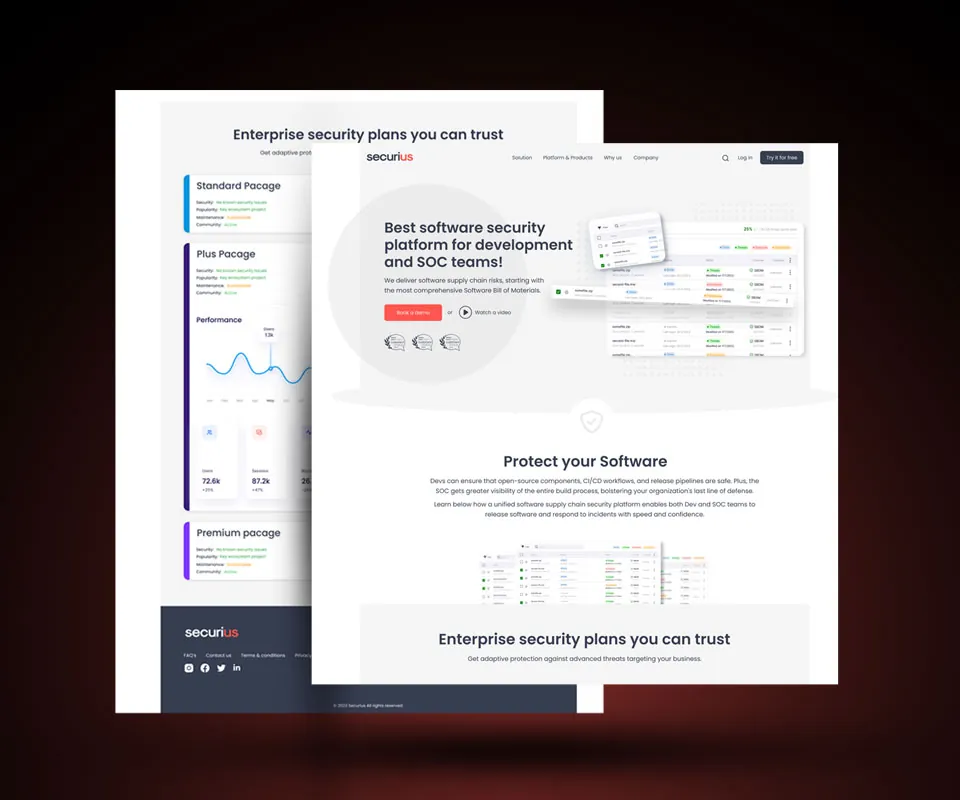
Overview
An engineer about to add an npm package can check its health score out of 100 and four signals covering security, popularity, maintenance and community.
The feature list goes further, with risk scoring, vulnerability reports, version history, dependency insights, security updates and activity tracking.
The work
The package report in the platform, then the landing page's plans section.
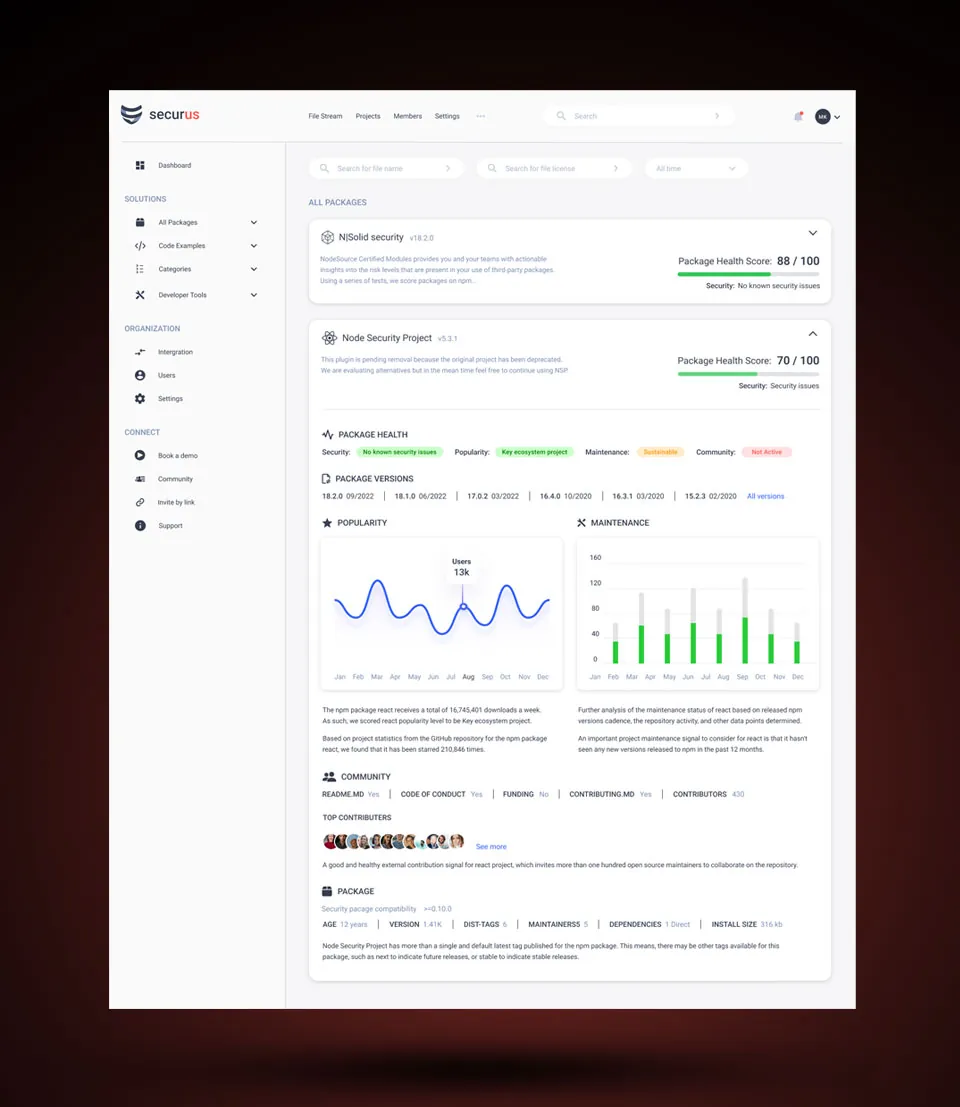
Package list and report
Each package in the list comes with its version, a short description, a health score bar and its security status.
In a report, the four signals come first as colored labels, so a weak one jumps out. Here, community is Not Active, in red. Under the popularity and maintenance charts, a few lines explain each label. Popularity covers weekly downloads and GitHub stars. For maintenance it's release cadence and repository activity.
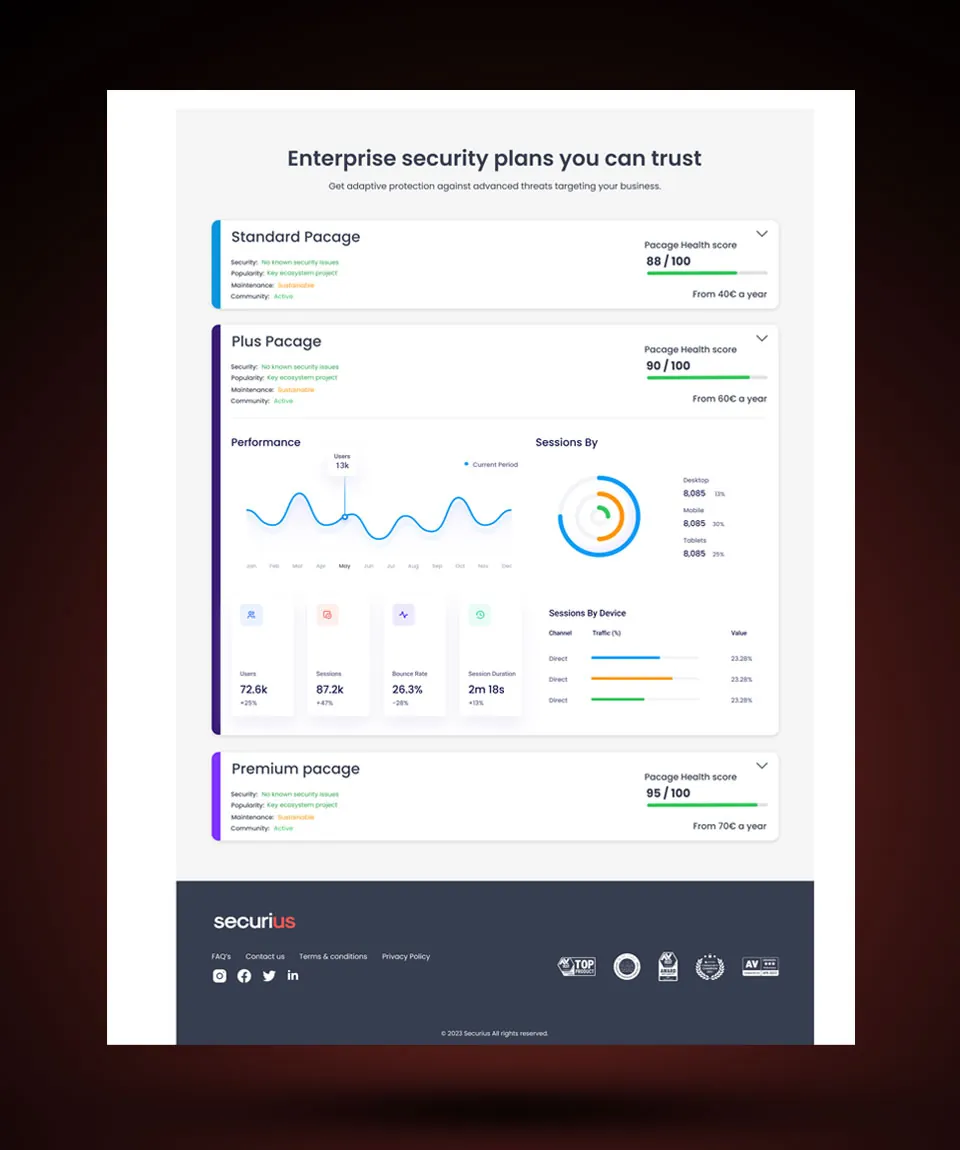
Security plans on the landing page
Standard starts at 40€ a year, Plus at 60€ and Premium at 70€. Each card has the four signals in color next to a health score bar, laid out like the package cards in the platform. A chevron expands it.
Here the Plus card is open on a performance panel, with a users chart, sessions by device and stat tiles such as bounce rate and session duration.
Contact
Let’s work together.
If you liked what you saw, or just want to say hi, drop me a line.